from-scratch operating system · in development
anonymOS
A capability-secured, object-graph OS with Qubes-style security domains, an immutable A/B-updated image, a native hypervisor, and a deniable install.
What it is
Every app runs in its own security domain.
anonymOS is a from-scratch x86-64 kernel written in D (-betterC, no GC). Every
task, file, window, identity and service is an object with capabilities in a validated
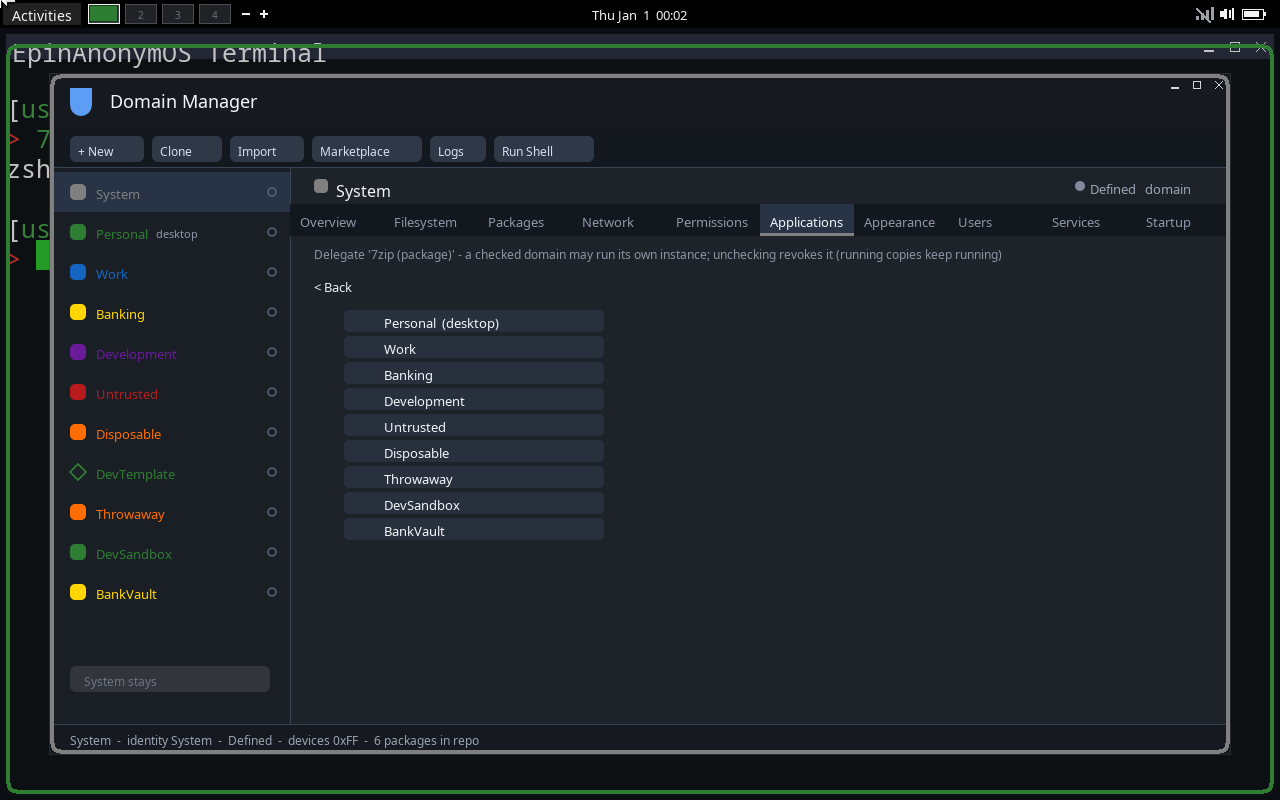
object-reference graph. Applications run confined in a domain — Personal, Work, Banking,
Development, Untrusted, Disposable, or one you create — each with its own identity,
files, network route and colour. The kernel refuses to run an app in a domain it was not
delegated to.
It boots a modern Wayland desktop (Hyprland) and runs unmodified Linux/musl programs such as Firefox, zsh and GTK apps through a Linux personality. It is actively developed and not yet verified on bare metal — the honest state of each part is on the features page.
Capability-secured domains
Seven built-in identities plus your own. A per-domain namespace, copy-on-write private
files, device and USB gates, and an appgate that only the Domain Manager can
change. Window titlebars are drawn by the compositor in each domain's colour, so an app
can't fake which domain it belongs to.
Immutable system, A/B updates
/usr is read-only and verified; /etc is an overlay. Plain
installs carry two system slots behind a UEFI A/B arbiter with retries and automatic
rollback. Updates are whole-image .hosupd units, Ed25519-verified against a
pinned key. Partial: plain installs only — encrypted installs have no A/B slots
yet.
Deniable, encrypted install
The installer offers a plain A/B install, full-disk XTS encryption, or a Hidden OS: a real decoy Linux (Alpine + XFCE) boots on the decoy password while the real system stays hidden in an encrypted outer volume. Every sector is erased first, and both paths take the same time.
Blockchain boot attestation
Turn on boot integrity and the installer records the system's boot-file hashes on-chain (an Ethereum testnet — Sepolia — during development). At boot the system proves itself against the live chain before the desktop starts, so an offline or sandboxed copy never boots. In development: end-to-end install-time deploy and boot-time gating are still being finished.
Native hypervisor & firewall VM
Intel VT-x with EPT and a KVM-compatible /dev/kvm let an unmodified Cloud
Hypervisor boot Linux and an OPNsense firewall VM. Each domain can route direct, through
the firewall VM, through another domain, or be blocked — and the routes persist.
Animated dendritic wallpaper
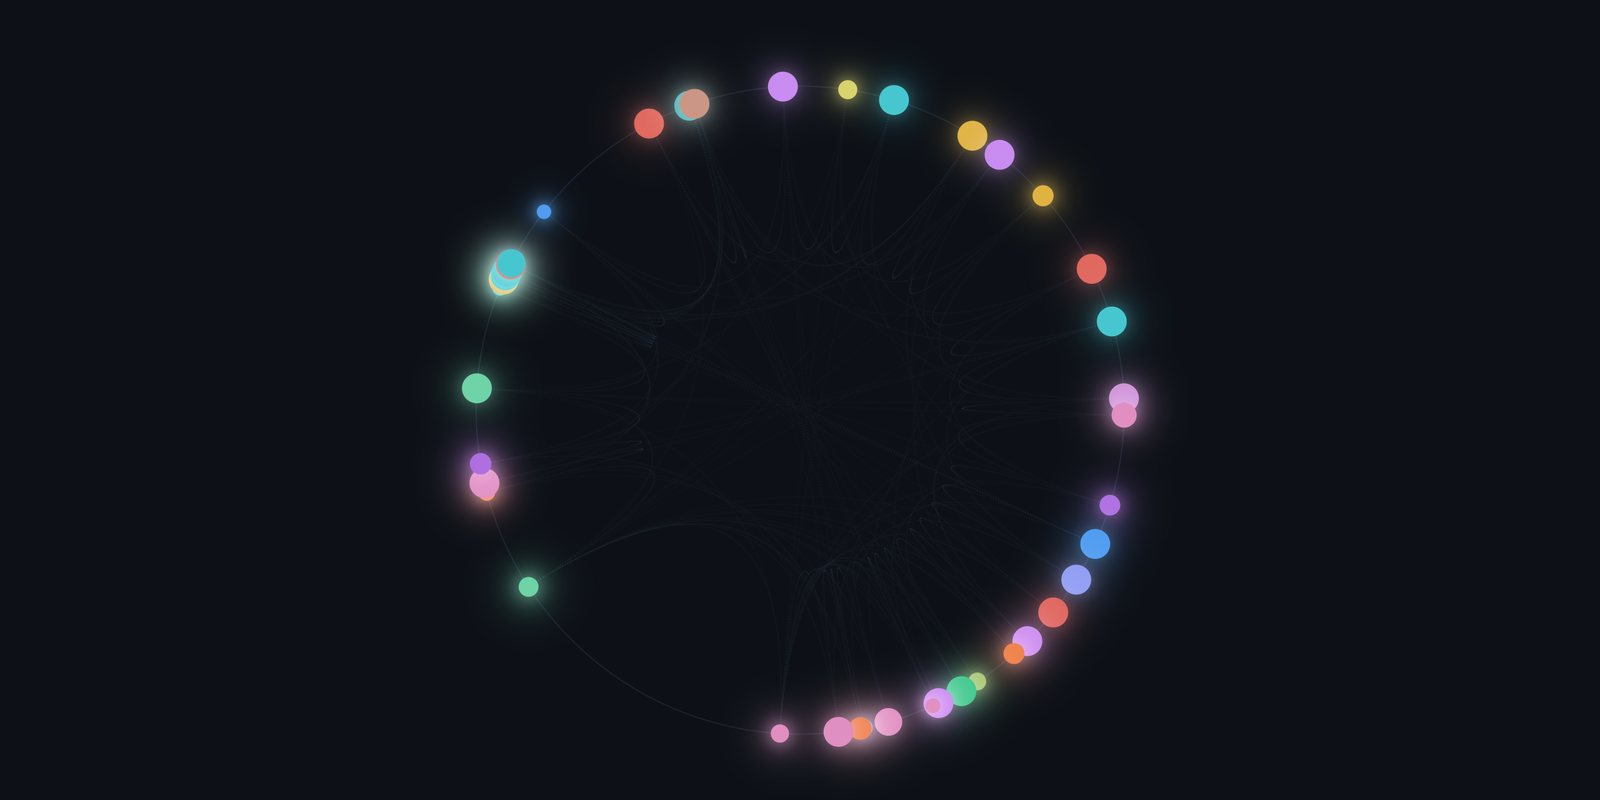
The desktop wallpaper is the animated dendritic "full canopy" — the branching tree you see above, pre-rendered into a sprite sheet and CPU-blitted frame by frame (28 frames, a seamless 3.5 s loop). No browser or GPU on the guest. Just added — it replaces the previous desktop widget.
Software Center
73,000+ packages in an offline catalog. Alpine main + community install system-wide with verified checksums and dependency resolution; installs survive reboots and are delegated to domains like any other app.
Memory hardening
W^X / NX by default, NX stacks, stack canaries in userspace and the kernel, full ASLR, mmap guard pages, SMEP and a heap double-free guard — each verified by booting the full desktop under it. Partial: SMAP infrastructure is in place but not yet enforced.
Screenshots
The real system.
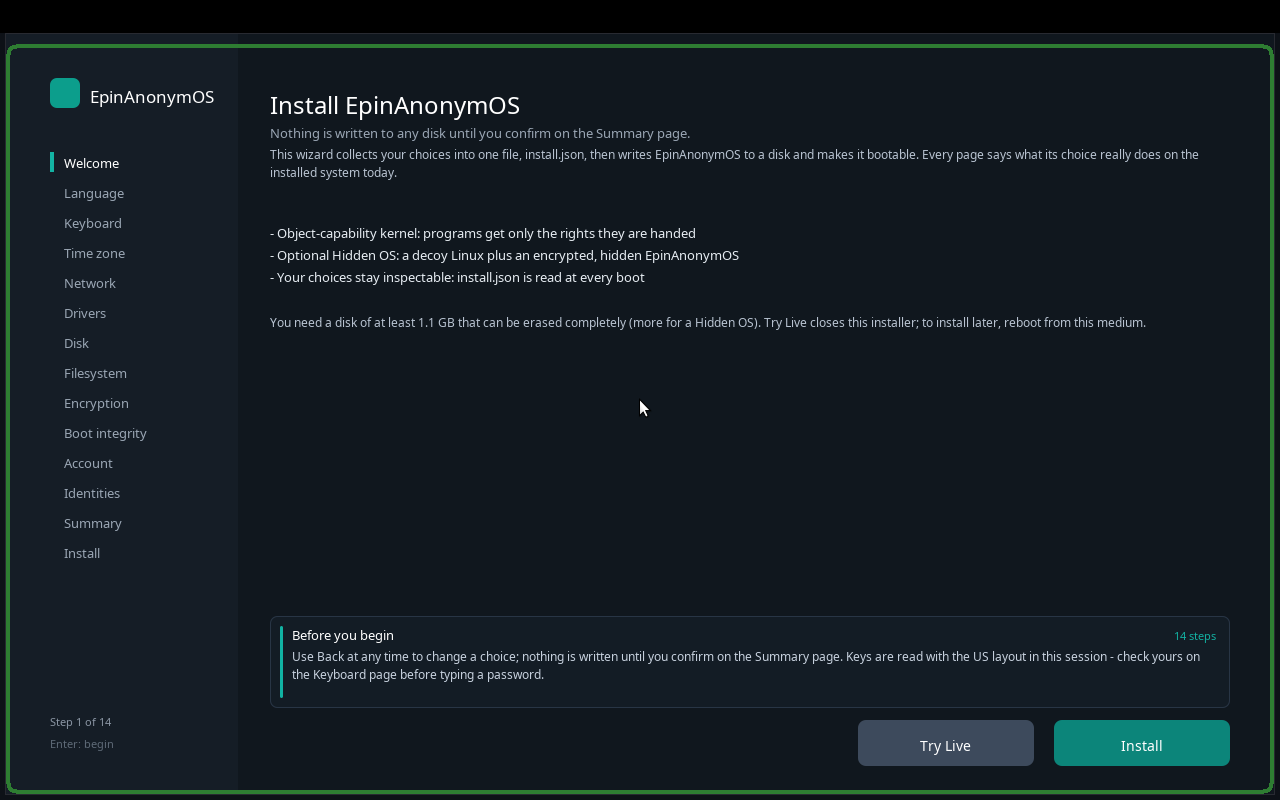
Captured from anonymOS running in a VM. Nothing here is a mock-up.
Get anonymOS
It builds from source into a bootable install ISO (hos-install.iso). There is
no hosted binary — you build the image yourself, or request the source.